Intercept X Endpoint

Endpoint Detection and Response (EDR)
Sophos Intercept X Advanced with EDR combines powerful Endpoint Detection and Response (EDR) with best-in-class malware and exploit protection. Intercept X was designed for both IT security operations and threat hunting, and detects and analyses suspicious activity using AI-driven analytics. Unlike other EDR tools, you get exclusive access to expert know-how that would normally require you to hire highly qualified analysts.

Anti-Ransomware

Deep Learning Technology
By integrating deep learning, a special form of machine learning, Intercept X turns reactive endpoint security into predictive endpoint security and reliably protects against unknown threats. Many vendors advertise that their products are based on machine learning. However, not all machine learning is the same. In the past, deep learning has consistently outperformed other machine learning models for detecting malware.

Exploit Prevention
Exploit Prevention stops the techniques used in fileless, malware-free and exploit-based attacks. Although millions of different malware variants are in circulation and thousands of software vulnerabilities exist, attackers use only a handful of exploit techniques as part of the attack chain. This is exactly where Intercept X comes in: the exploit techniques are specifically blocked and zero-day attacks are stopped in their tracks.

Managed Threat Response

Active Adversary Mitigations
Intercept X uses a range of techniques, including Credentials Theft Prevention and Code Cave Utilization Detection, to prevent attackers from gaining a foothold in networks and remaining undetected there. Attackers are increasingly focusing on techniques that go beyond malware in order to move through systems and networks as legitimate users. Intercept X detects and stops this behaviour.
Deep Learning
Intercept X uses deep learning neural networks, which are a special form of machine learning, to provide even more security for your endpoints. This means that even unknown malware can be identified as malicious software without signatures.
Thanks to deep learning, Intercept X has an enormous advantage over conventional endpoint security solutions that rely on standard machine learning or signature-based detection.

Effective Removal of Ransomware
Intercept X blocks ransomware attacks before they can cause serious damage to your company. Malicious encryption processes are detected as quickly as possible and their spread across the network is prevented.
If files have already been encrypted, they are restored to their safe state. In this way, Intercept X enables an uninterrupted intervention during the working day and ensures the continuity that you and your company need.
Synchronisation between Software and Hardware
You achieve optimum security through the interaction of Intercept X Endpoint Security and your XG Firewall. With Synchronized Security, you enable these two security components to exchange information in real time and thus respond even faster and more effectively to attacks and incidents.

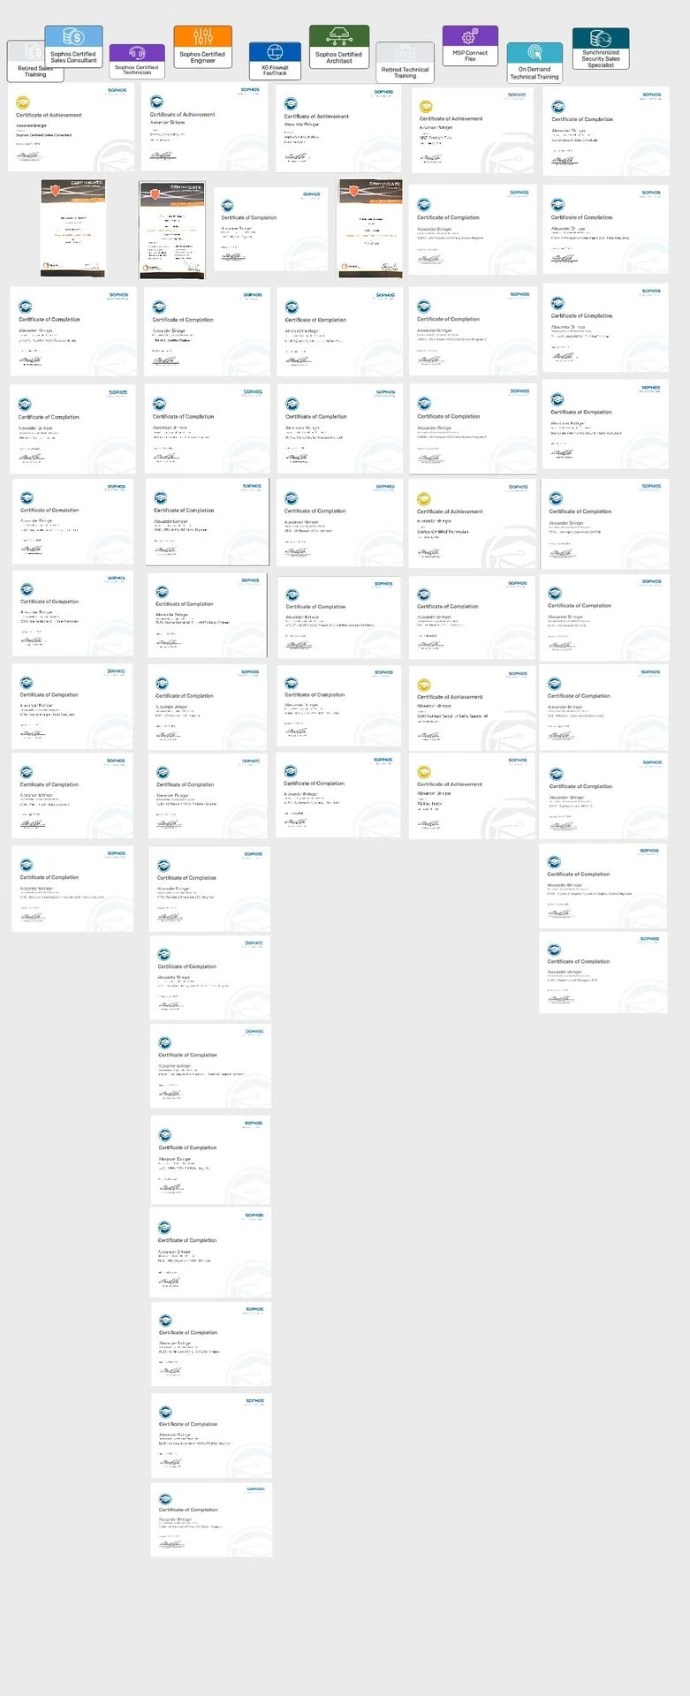
Trust a certified Partner
We have been on board with Sophos, formerly Astaro, from the very beginning. Here you receive first-class support from a consistently certified support team.
The team, consisting of Alexander, Dominic, Robert and Nanti, holds continuous certification in all areas. Nisa also covers the commercial side for the back office, which all technicians are also proficient in.